

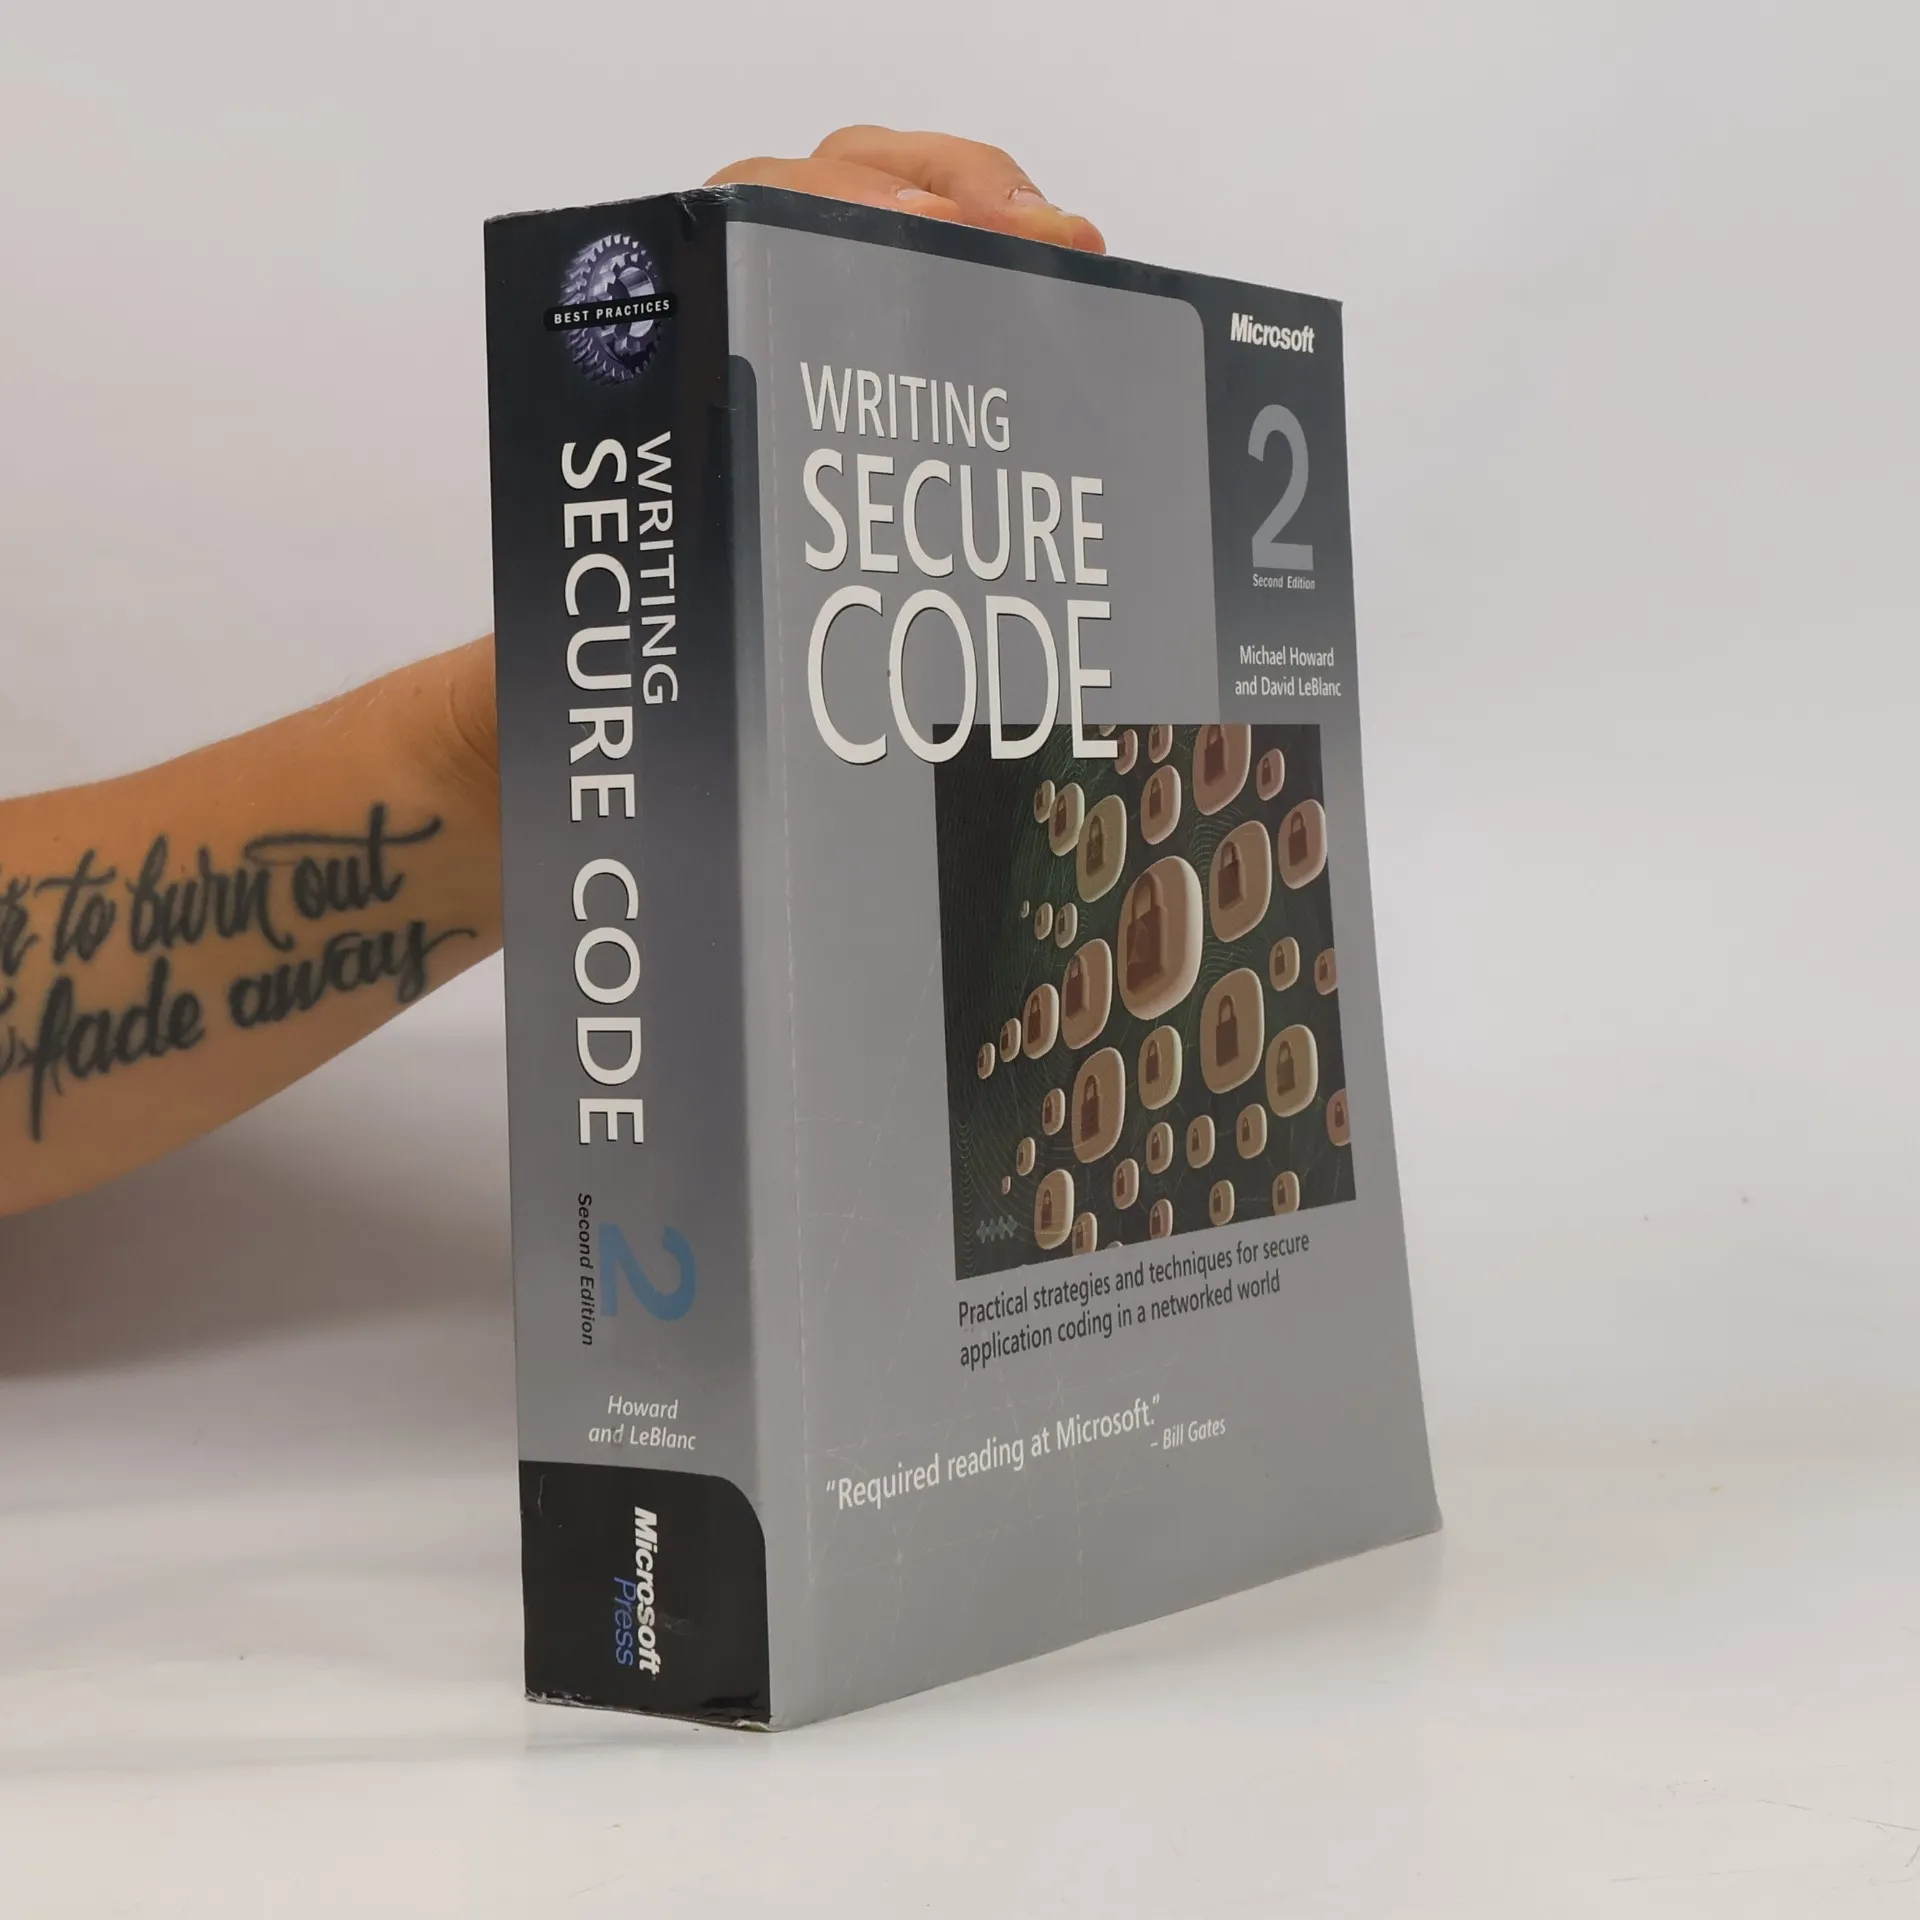
Writing Secure Code
Practical Strategies and Techniques for Secure Application Coding in a Networked World - Second Edition
Hodnocení knihy
Více o knize
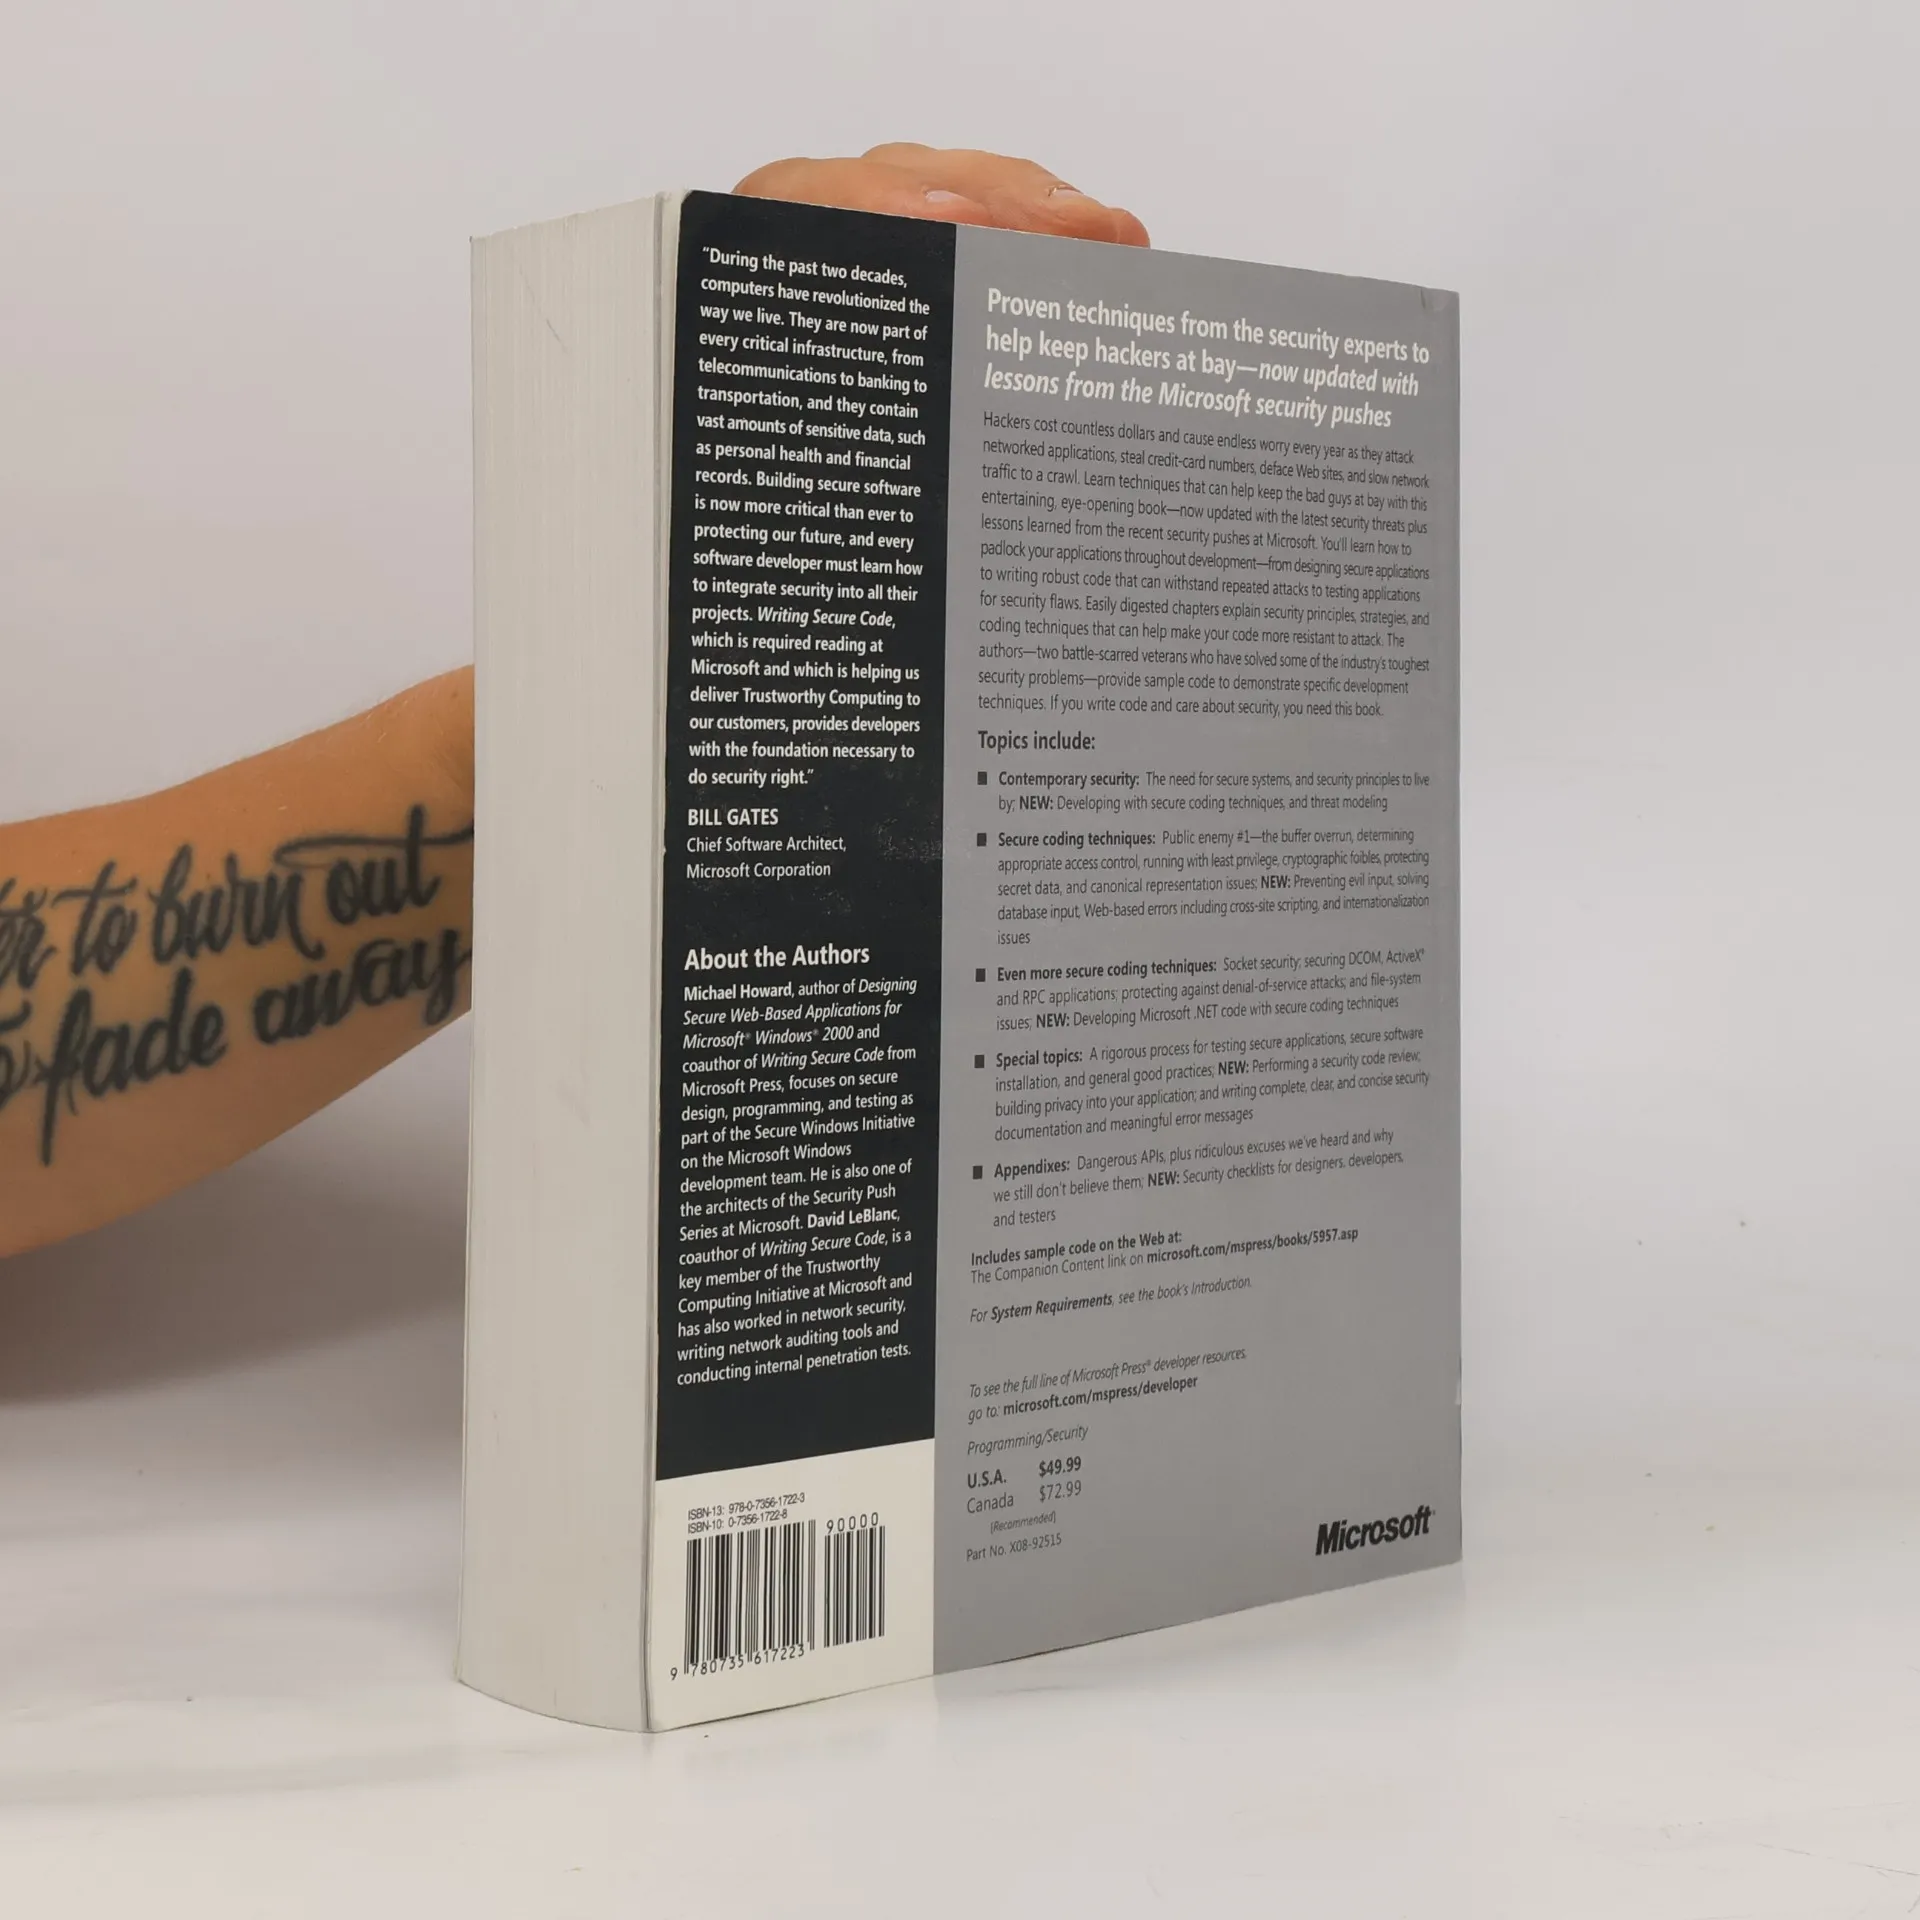
Your code will be attacked. You need to design, code, and test with the assumption that it will run in hostile environments. This book shows you how, drawing on lessons from Microsoft's 2002 Windows Security Push. It significantly upgrades the First Edition with new insights. The authors help you define security for your customers and implement a strategy focusing on design, defaults, and deployment. A key feature is threat modeling, which involves breaking down your application, identifying threats, ranking them, and mitigating them. The book delves into critical security issues from a developer's perspective, including a full chapter on avoiding buffer overruns. You'll learn to establish proper access controls and adopt a least privilege approach. There’s also detailed guidance on countering cryptography attacks, such as avoiding poor random numbers and bit-flipping. The book offers countermeasures for various user input attacks, including malicious database updates and cross-site scripting. Techniques for securing sockets, protecting against DOS attacks, building safer .NET applications, and writing high-quality security documentation are also covered. Following these techniques will enhance security and significantly improve robustness and reliability.


Nákup knihy
Writing Secure Code, Michael Howard, David LeBlanc
- Jazyk

- Rok vydání
- 2005
- Vazba
- (měkká)
Tady nám chybí tvá recenze.
- Titul
- Writing Secure Code
- Podtitul
- Practical Strategies and Techniques for Secure Application Coding in a Networked World - Second Edition
- Jazyk
- anglicky
- Autoři
- Michael Howard, David LeBlanc
- Vydavatel
- Microsoft Press
- Rok vydání
- 2005
- Vazba
- měkká
- Počet stran
- 768
- ISBN10
- 0735617228
- ISBN13
- 9780735617223
- Série
- Štítky
- Příručky a návody, Technologie, Software, Tvorba webu, Vývoj softwaru, Bezpečnost na internetu
- Původní název
- Writing Secure Code & Writing Secure Code for Windows Vista
- Hodnocení
- 3,25 z 5
- Anotace
- Your code will be attacked. You need to design, code, and test with the assumption that it will run in hostile environments. This book shows you how, drawing on lessons from Microsoft's 2002 Windows Security Push. It significantly upgrades the First Edition with new insights. The authors help you define security for your customers and implement a strategy focusing on design, defaults, and deployment. A key feature is threat modeling, which involves breaking down your application, identifying threats, ranking them, and mitigating them. The book delves into critical security issues from a developer's perspective, including a full chapter on avoiding buffer overruns. You'll learn to establish proper access controls and adopt a least privilege approach. There’s also detailed guidance on countering cryptography attacks, such as avoiding poor random numbers and bit-flipping. The book offers countermeasures for various user input attacks, including malicious database updates and cross-site scripting. Techniques for securing sockets, protecting against DOS attacks, building safer .NET applications, and writing high-quality security documentation are also covered. Following these techniques will enhance security and significantly improve robustness and reliability.