

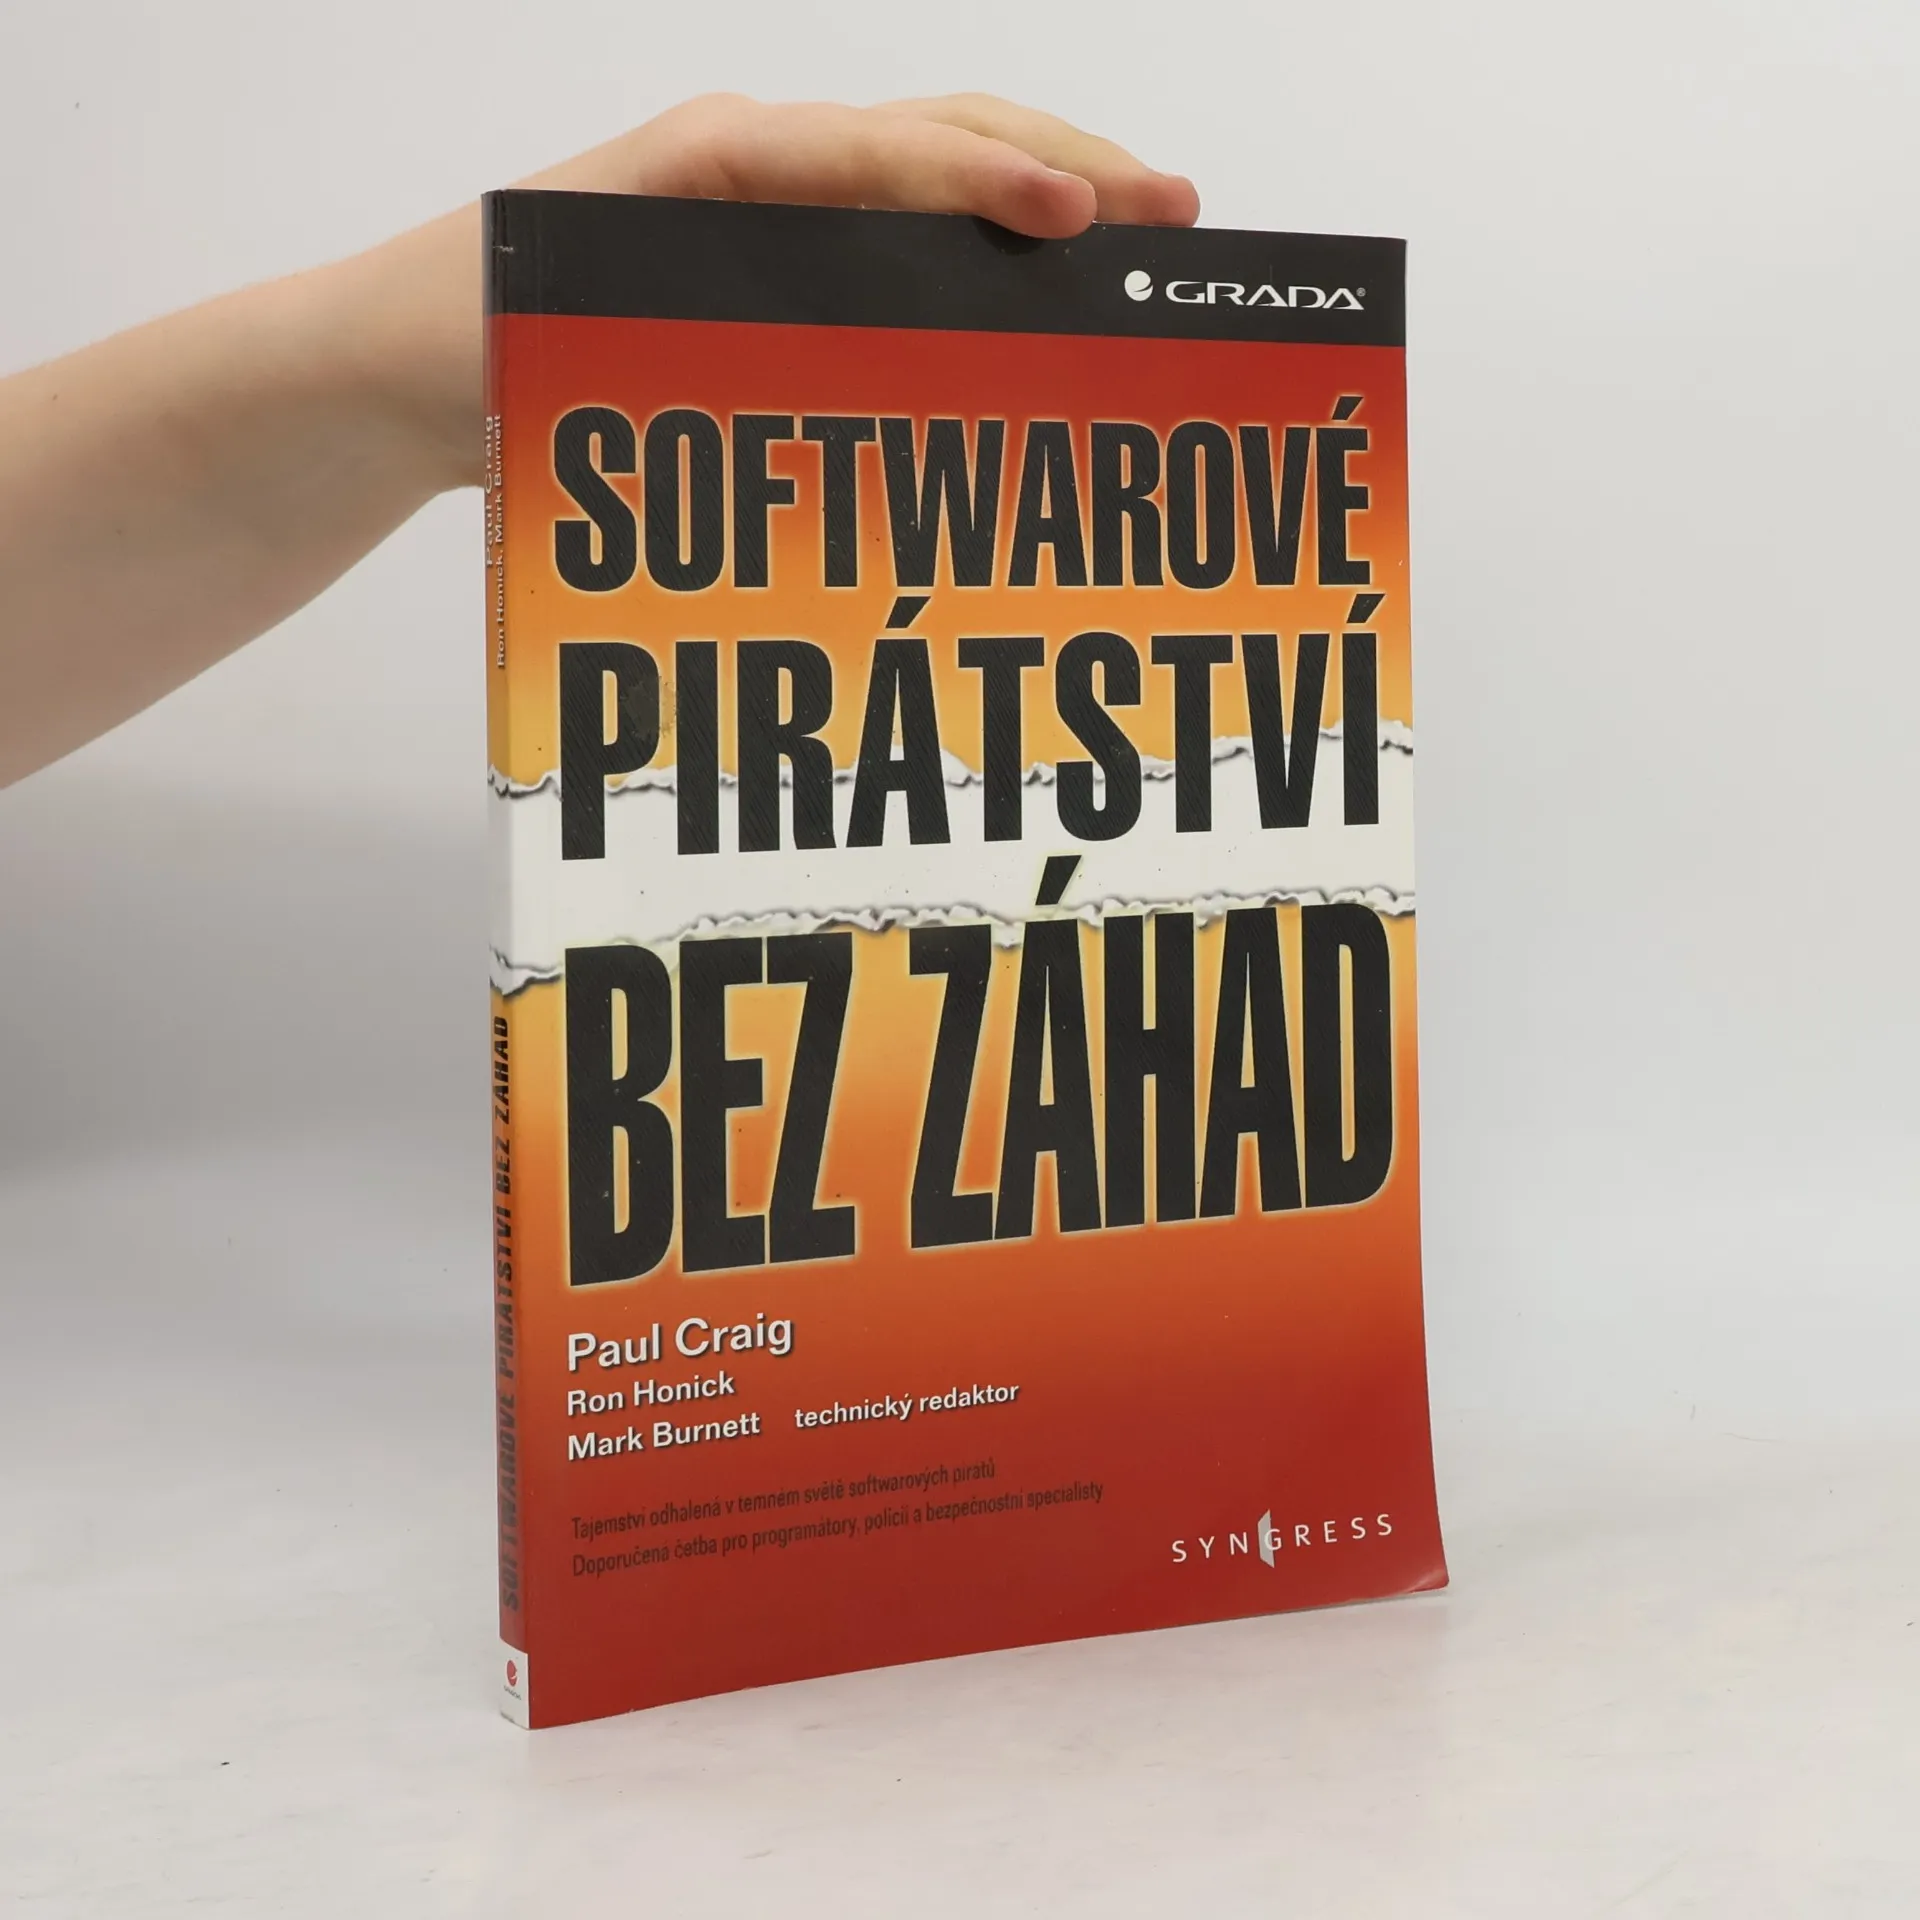
Chcete-li se na vlastní riziko ponořit do technik softwarového pirátství, které vás zaručeně dostanou za mříže, pak neváhejte a sáhněte po této knize. Nenaučí vás, jak se bránit nelegální činnosti, ale nahlédnete pod pokličku toho "jak to dělají" crackeři, kurýři a softwaroví piráti či co znamená warez. Autor vám na základě vlastního vyšetřování předvede, jak crackeři tráví desítky hodin rozlomením kódů, umožní analyzovat cesty, kudy proudí pirátský software od crackera ke konečnému uživateli, ale také, jak tvrdě některé země postupují proti těmto technikám. Tato výjimečná kniha je napříč protnuta záznamy chatů s nejvýraznějšími osobnostmi mezinárodní pirátské scény.
Mark Burnett Knihy



Son of God
- 144 stránek
- 6 hodin čtení
This book narrates some of the most important episodes from the Scriptures, from the creation of man to Jesus' time on Earth. With an engaging narrative and a dynamic text, Roma Downey and Mark Burnett bring to life great characters - Moses, David, Samuel, Samson - and describe fundamental passages from the sacred book, such as the flood that devastated the planet's first inhabitants, God's promise to Abraham, the ten plagues of Egypt, Judas' betrayal, and the apostles' struggle to keep the Messiah's message alive. Electrifying like a suspense novel, moving like the most beautiful romance of all time, this book will captivate even those who never imagined being excited by the stories of the Bible.
Security Log Management
- 350 stránek
- 13 hodin čtení
This book instructs IT professionals on how to analyze, manage, and automate security log files to create useful, repeatable insights that enhance network efficiency and security, primarily using open source tools. It starts by identifying the "Top 10" security logs that should be regularly analyzed, covering key areas such as the most active workstations and primary targets of IDS alerts. The relevance of this information is then discussed. The book also explains how to use open source reporting tools like Tcpdstats to automate the correlation of log files from various network devices with the "Top 10" list, enabling IT professionals to quickly identify critical vulnerabilities or significant network performance issues. All scripts featured in the book are available for download from the Syngress Solutions website. Nearly every operating system, firewall, router, switch, intrusion detection system, mail server, web server, and database generates log files, making log analysis a common task for system administrators and security professionals. This resource provides cost-effective, open source solutions for evaluating network performance and security, with numerous working scripts and tools that can save administrators countless hours by automating both simple and complex log analysis tasks.
Jump In!
- 288 stránek
- 11 hodin čtení
The executive producer of such hits as "Survivor" shares the story of his own rise from obscurity to the heights of the entertainment world, imparting advice on how to achieve personal and professional success.
Microsoft Log Parser Toolkit
A Complete Toolkit for Microsoft's Undocumented Log Analysis Tool
- 437 stránek
- 16 hodin čtení
Written by Microsoft's Log Parser developer, this is the first book available on Microsoft's popular yet undocumented log parser tool. The book and accompanying Web site contain hundreds of customized, working scripts and templates that system administrators will find invaluable for analyzing the log files from Windows Server, Snort IDS, ISA Server, IIS Server, Exchange Server, and other products. System administrators running Windows, Unix, and Linux networks manage anywhere from 1 to thousands of operating systems (Windows, Unix, etc.), Applications (Exchange, Snort, IIS, etc.), and hardware devices (firewalls, routers, etc.) that generate incredibly long and detailed log files of all activity on the particular application or device. This book will teach administrators how to use Microsoft's Log Parser to data mine all of the information available within these countless logs. The book teaches readers how all queries within Log Parser work (for a Log Parser query to an Exchange log may provide information on the origin of spam, viruses, etc.). Also, Log Parser is completely scriptable and customizable so the book will provide the reader with hundreds of original, working scripts that will automate these tasks and provide formatted charts and reports detailing the results of the queries.